


[2026] Use Valid VNX301 Exam - Actual Exam Question & Answer
Test Engine to Practice VNX301 Test Questions
NEW QUESTION # 36
Which two statements are true about templates? (Choose two.)
- A. You can have more than one device template per appliance.
- B. You must have at least one service template per appliance.
- C. You can use a Workflow Template to create new device templates.
- D. You can use variables in a template to allow devices to have unique values.
Answer: C,D
Explanation:
The correct answers are C and D . Versa templates are designed to reuse common configuration while still allowing per-device customization. Template variables allow the same template to be deployed to multiple appliances while using device-specific values such as addresses, VLAN IDs, DHCP information, or other bind-data values. Versa documentation for deploying templates describes assigning values to variables contained in a main template that are specific to the device. This makes option C correct.
Option D is also correct because Versa workflows are used to create templates for VOS device configuration.
Versa documentation states that workflows are used to create templates to configure VOS devices, and also to create templates for application steering, spoke groups, and service chains.
Option A is not correct in the normal Versa Director onboarding model because a group of devices is associated with one staging template and one post-staging template, rather than multiple device templates being stacked per appliance. Option B is also incorrect because service templates are optional reusable service-specific fragments. Versa documentation states that service templates can be used by multiple device templates and device groups, but it does not require every appliance to have one.
NEW QUESTION # 37
You are configuring the BGP routing protocol between a Versa Secure SD-WAN CPE with AS number
64514 and two upstream service providers: SP1 with AS number 64515 and SP2 with AS number 64519. You want to prefer BGP routes learned from AS 64515 over routes learned from AS 64519. Which BGP path attribute would be used to accomplish this task?
- A. The BGP MULTI_EXIT_DISC path attribute
- B. The BGP NEXT_HOP path attribute
- C. The BGP LOCAL_PREF path attribute
- D. The BGP ORIGIN path attribute
Answer: C
Explanation:
The correct answer is LOCAL_PREF . In BGP, the Local Preference attribute is used inside an autonomous system to influence which exit path is preferred for outbound traffic. In this scenario, the Versa Secure SD- WAN CPE receives routes from two upstream service providers, SP1 and SP2. To prefer routes learned from AS 64515 over routes learned from AS 64519, you would apply a BGP import or route policy that assigns a higher local preference to routes received from SP1. Versa SD-WAN design guidance shows this exact routing concept: an import policy can manipulate the Local-Pref attribute to prefer one advertised route path over another. The Versa output examples also display "Local Preference" as a BGP route attribute used in route selection.
MULTI_EXIT_DISC, or MED, is generally used to influence how a neighboring AS enters your AS, not how your CPE prefers routes learned from different upstreams. ORIGIN is part of BGP best-path selection but is not normally the administrative tool used to prefer one provider. NEXT_HOP identifies the next-hop address and does not directly define route preference.
NEW QUESTION # 38
A branch has Direct Internet Access enabled. Users can resolve DNS, but application traffic fails. You find that the internet speed test also fails to fetch the server list. Which two configurations should be checked first?
- A. SNMP community and syslog server
- B. VRRP priority and DHCP lease time
- C. CGNAT and DNS configuration
- D. OSPF area ID and BGP MED
Answer: C
Explanation:
The correct answer is A . Versa documentation for internet speed tests states that before running an internet speed test, administrators must verify WAN internet connectivity and verify that CGNAT is configured on the provider organization. It also states that administrators should verify that they can retrieve the list of predeployed internet speed-test servers. If an error occurs while fetching the server list, the documentation instructs administrators to check the CGNAT and DNS configurations and then click Fetch Server List again.
This aligns with the scenario because DNS resolution and internet breakout depend on correct DNS reachability, NAT translation, and routing through the internet-facing transport. Even if DNS appears partially functional, CGNAT misconfiguration can still prevent application or HTTP test traffic from completing properly.
OSPF, BGP MED, SNMP, syslog, VRRP, and DHCP may be important in other designs, but they are not the first items Versa identifies for a failed internet speed-test server-list fetch in a DIA context.
NEW QUESTION # 39
A branch device is stuck after staging. The Controller does not show the expected branch lifecycle notification. Which statement best describes the role of MP-BGP in the provider organization for this process?
- A. MP-BGP is required only for URL filtering category updates.
- B. MP-BGP is recommended so notifications for relevant branch events are delivered to Versa Director.
- C. MP-BGP replaces IKE and IPsec during branch staging.
- D. MP-BGP is used only between branch LAN routers and user subnets.
Answer: B
Explanation:
The correct answer is A . Versa branch troubleshooting documentation states that the provider organization should have MP-BGP configured for SD-WAN deployments so that notifications for all relevant branch events are delivered to the Versa Director node. This is significant during onboarding because branch lifecycle events, such as branch-connect and branch-disconnect, help Director determine where the branch is in the staging process and whether the next configuration push should occur.
MP-BGP does not replace IKE or IPsec. The branch still establishes IKE/IPsec to the staging server or Controller depending on the staging phase. MP-BGP also has nothing to do with URL filtering category updates. While BGP can be used in LAN or WAN routing designs, the specific issue described here concerns provider-organization SD-WAN control-plane event delivery.
Therefore, if branch lifecycle events are not appearing properly, validating provider-organization MP- BGP configuration is part of the correct troubleshooting workflow, especially in addition to checking data-path and IPsec connectivity.
NEW QUESTION # 40
Examine the exhibit below.
Which two statements correctly explain the routing shown in the exhibit. (Choose two.)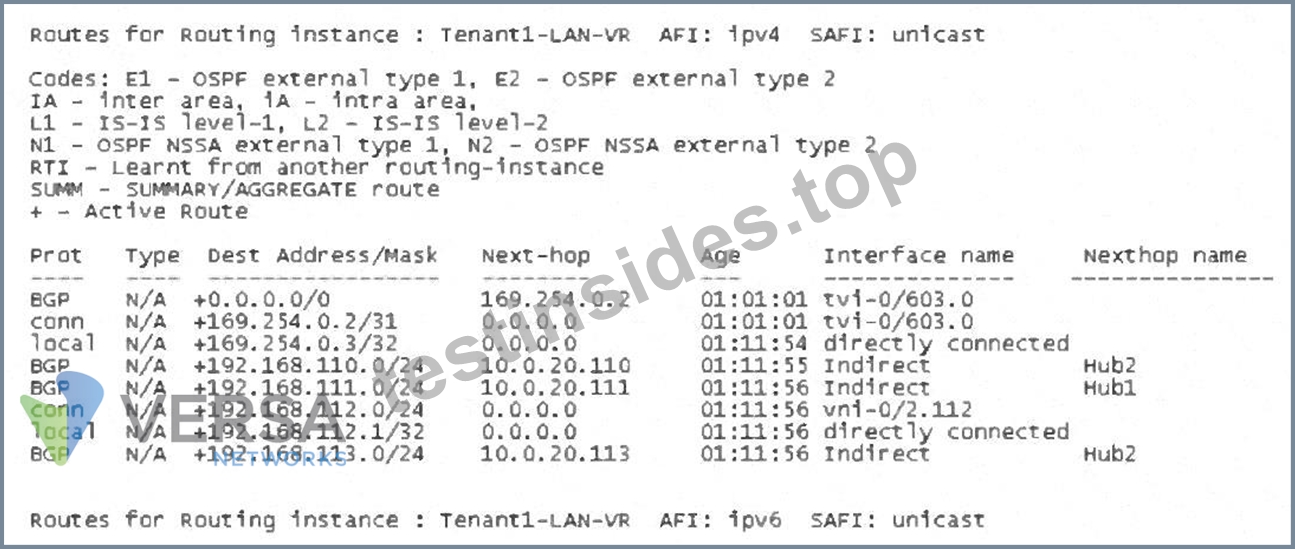
- A. The tvi-0/603 interface is a stub interface for black holing an unknown IP unicast destination.
- B. Any unknown IP unicast destination will use the tvi-0/603 interface for its exit.
- C. The tvi-0/603 interface is paired with an interface in another VR for the default route.
- D. The IP address configured on the tvi-0-603 interface its misconfigured by the template.
Answer: B,C
Explanation:
The correct answers are A and C . The route table shown in the Versa SD-WAN design documentation includes a default route, 0.0.0.0/0 , with next hop 169.254.0.2 and exit interface tvi-0/603.0 . A default route is used when no more specific route exists in the routing table, so any unknown IPv4 unicast destination will follow that active default route through the tvi-0/603 interface. This directly supports option C.
The same design context describes local or central internet breakout, where Director workflows create TVI- based connectivity for breakout or gateway-style forwarding. In Versa SD-WAN, TVI interfaces are commonly used as internal virtual tunnel interfaces between routing instances, such as between a tenant LAN VR and a transport or breakout VR. The documentation also describes virtual TVI interface pairs being created by Director workflows between VRs for gateway routing use cases. Therefore, option A is also correct: tvi-0/603 is paired with another interface in another VR to support the default-route forwarding path.
The IP address is not shown as misconfigured; 169.254.x.x addressing is commonly used for point-to- point internal TVI links. The route is also not a blackhole route, because it has an active next hop and an exit interface.
NEW QUESTION # 41
What are two features of the Stateful Firewall service in the Versa Operating System? (Choose two.)
- A. Intrusion Detection System
- B. URL filtering
- C. Application-Level Gateways (ALG)
- D. DoS protection
Answer: C,D
Explanation:
The correct answers are A and D . Versa stateful firewall service includes classic firewall functions that track sessions and enforce traffic policy, and it can work with DoS policy enforcement. Versa's CLI guide includes Configuring DoS policies under the security configuration area, where DoS rules can match on source, destination, services, applications, URL category, IP version, DSCP, TTL, EtherType, and other packet or session attributes, and can then apply aggregate or classified DoS profiles. This validates DoS protection as a stateful firewall/security service capability.
Application-Level Gateways, or ALGs , are also associated with stateful firewall/NAT behavior because they inspect and assist protocol handling for applications that embed addressing or dynamic port information inside the payload or control channel. This is part of traditional stateful firewall service behavior rather than UTM content inspection.
NEW QUESTION # 42
A tenant uses CGNAT for internet breakout. You want to verify whether CGNAT rules, pools, static NAT entries, subscribers, and endpoint-independent mapping entries are programmed in the vsmd daemon for a tenant. Which command should you use after connecting to vsmd?
- A. show cgnat tenants
- B. show interfaces brief
- C. show alarms last-n 20
- D. show system uptime
Answer: A
Explanation:
The correct answer is A . Versa CGNAT troubleshooting documentation provides commands to inspect CGNAT state inside the vsmd daemon. To view summary information about configured tenants, the document instructs administrators to issue show cgnat tenants . The sample output shows each tenant ID and counters such as the number of configured rules, pools, DS-Lite service chains, 6RD service chains, static NAT entries, subscribers, endpoint-independent mapping entries, endpoint-independent filtering entries, and softwires.
This command is especially useful when CGNAT configuration appears correct in Director but translation is not happening, because it confirms whether the runtime dataplane process actually has the tenant CGNAT state.
show interfaces brief shows interface status and IP addressing. show alarms shows event notifications, and show system uptime shows how long the system has been running. These are useful operational commands but do not show CGNAT tenant programming inside vsmd.
NEW QUESTION # 43
Examine the exhibit below.
The exhibit shows a device group created for a new group of hubs. The device template called "BMBF- TEMPLATE" has an Address object called "Server". A network administrator creates the Class of Service Template called "Ship-CoS-IT" that has an Address object with the same name. Then it tries to onboard a new device to this device group.
Which statement is true about the configuration that this device will have?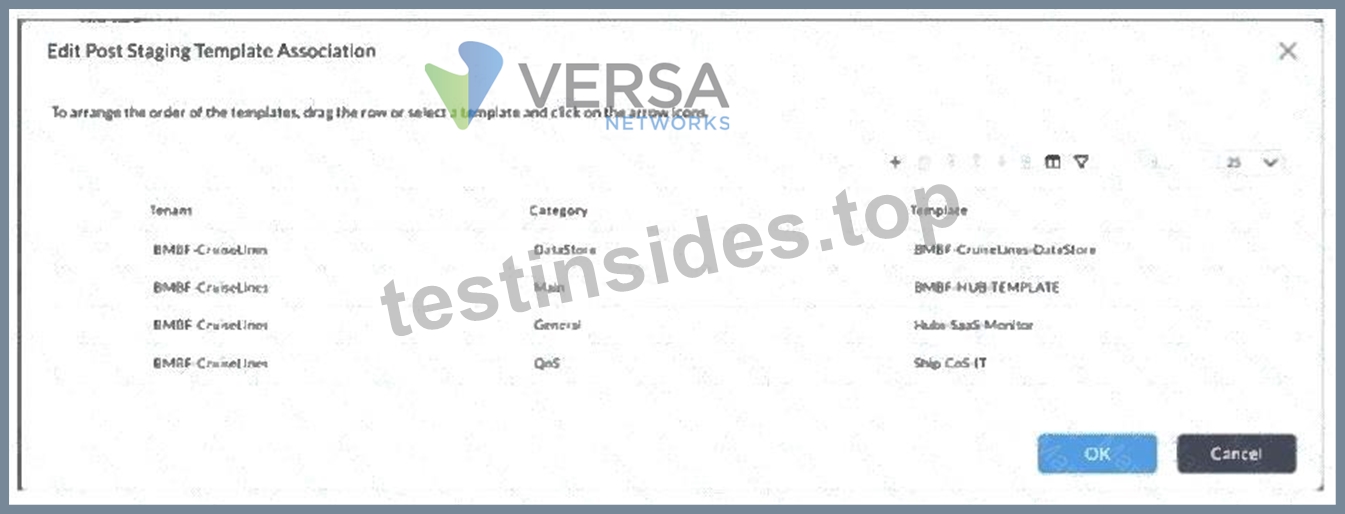
- A. The device configuration will automatically create two copies of the same Address object.
- B. The device configuration will have the version of the Address object in the QoS template.
- C. The device configuration commit will fail.
- D. The device configuration will have the Address object that was created last.
Answer: B
Explanation:
The correct answer is D . In the displayed post-staging template association order, the device template BMBF- TEMPLATE is applied before the QoS service template Ship-CoS-IT . Versa documentation explains that device templates, also called post-staging templates, provide the baseline configuration for devices, while service templates are service-specific configurations that can be applied to device configurations. It also states that service templates are associated with device groups and that, in a device group, the administrator can choose the order in which service templates are applied.
Because the QoS template is later in the shown association order, the final merged device configuration uses the Address object definition from the QoS template when the same object name exists in both templates. It does not automatically create two copies of the same Address object, because the object name is the key for the configuration element. It also should not fail merely because the same object name exists in a later template; the merge behavior resolves the effective configuration according to the template order. Therefore, the onboarded hub device receives the Server Address object version from Ship-CoS-IT, the QoS template.
NEW QUESTION # 44
You are configuring a CGNAT rule for branch internet access and want to verify which access-list entry will match traffic before translation. Which information is shown by the CGNAT ACL command?
- A. Only system uptime and CPU usage
- B. Only SD-WAN SLA latency, jitter, and loss
- C. Only BGP AS path and local preference
- D. Rule ID, category, precedence, VRF, source IP, and destination IP
Answer: D
Explanation:
The correct answer is A . Versa CGNAT troubleshooting documentation shows the command show cgnat acl info < tenant-id > for viewing CGNAT access lists used for traffic matching. The example output includes columns such as ACL handle , RuleId , Category , Precedence , VRF , Source IP , and Destination IP . It also shows tenant ID and total filters.
This command is useful when a CGNAT rule exists in configuration but sessions are not being translated. By checking the ACL output, the administrator can confirm whether the correct source prefix, destination prefix, VRF, and rule precedence are actually programmed in the dataplane. If the wrong VRF or subnet is shown, the rule may never match the intended traffic.
System uptime and CPU usage are operational health indicators. SLA metrics are SD-WAN path- quality values. BGP AS path and local preference are routing attributes. None of these directly show CGNAT access-list match programming.
NEW QUESTION # 45
A CGNAT rule is configured, but traffic is not being translated. You want to confirm whether the expected source and destination prefixes are programmed in the CGNAT access list for the tenant. Which command is most appropriate?
- A. show device clients
- B. show system storage
- C. show cgnat acl info < tenant-id >
- D. show system status
Answer: C
Explanation:
The correct answer is A . Versa CGNAT troubleshooting documentation states that, after connecting to the vsmd daemon, administrators can view CGNAT access lists used for traffic matching with the command show cgnat acl info < tenant-id > . The sample output shows ACL handle, rule ID, category, precedence, VRF, source IP, destination IP, tenant ID, and total filters.
This is the correct command when NAT configuration appears present but translations do not occur, because it verifies whether the runtime dataplane has the correct traffic-match rules. If the source prefix, destination prefix, VRF, or precedence is wrong, the session may never match the NAT rule, and no translation will be applied.
show system status checks system services. show device clients shows active and failed sessions, CPU usage per session, and memory load for processes. show system storage shows disk usage. These commands are useful in other troubleshooting workflows, but they do not validate CGNAT ACL matching criteria for tenant traffic.
NEW QUESTION # 46
Examine the exhibit below.
As an administrator of a Versa Secure SD-WAN, you are asked to find the current bandwidth of each WAN circuit used for SD-WAN connectivity in a branch, but the Director is not displaying any information for the WAN circuits.
In this scenario, what should be done to get the graph populated for all WAN circuits?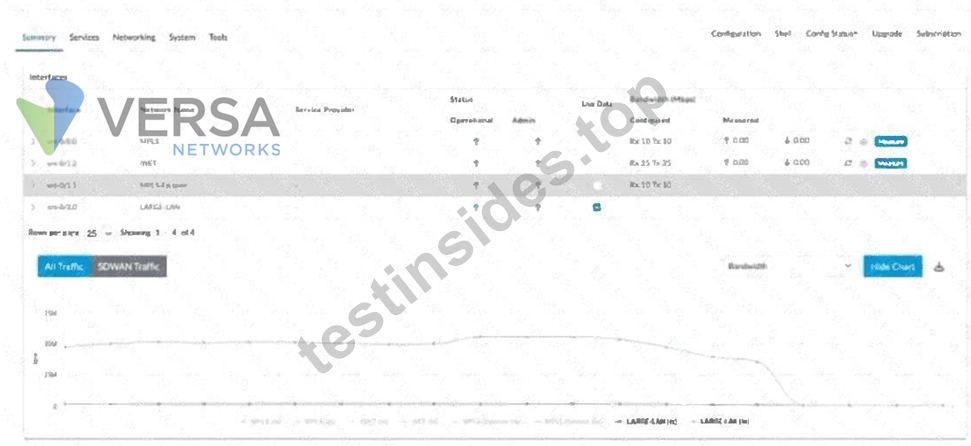
- A. Refresh the page to get the graphs populated in the dashboard.
- B. Unselect live data for INET circuit and select again. group
- C. Select live data for MPLS circuits alone.
- D. Select live data for all WAN circuits in the dashboard.
Answer: D
Explanation:
The correct answer is B . The exhibit shows the branch interface summary in Versa Director with a Live Data column. To populate real-time bandwidth graphs for WAN circuits, the administrator must select Live Data for the WAN interfaces that need to be monitored. Versa monitoring documentation states that, from a Director node, you can monitor VOS devices and organizations, and that Director, together with Versa Analytics, can poll VOS devices in real time to understand what is happening on the devices. This real-time information can be displayed to assist with troubleshooting.
Because the question asks for the current bandwidth of each WAN circuit, historical analytics alone is not sufficient. The dashboard must poll live statistics from the selected WAN circuits. In the exhibit, not all WAN interfaces appear to have Live Data selected; therefore, the graph is not populated for all circuits. Refreshing the page does not enable polling and will not solve the missing data condition.
Selecting only MPLS would populate only the MPLS circuit, not all WAN circuits. Unselecting and reselecting only the INET circuit would affect only that one interface. Therefore, Live Data must be selected for all WAN circuits whose current bandwidth should be displayed.
NEW QUESTION # 47
Examine the exhibit below.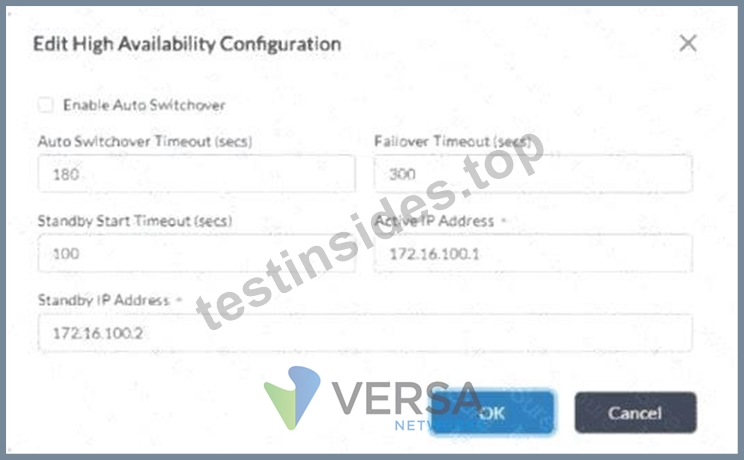
You are deploying Versa Secure SD-WAN and require high availability for the Versa Directors. You configured the Versa Director high availability parameters shown in the exhibit. With the parameters shown, which two statements are true? (Choose two.)
- A. The backup Director will automatically take over mastership if the primary Director fails.
- B. The administrator must manually set the primary Director as active once it comes back online.
- C. The primary Director will automatically take over mastership once it comes back online.
- D. The administrator must manually initiate the failover to the backup Director.
Answer: A,B
Explanation:
Comprehensive and Detailed 150 to 250 words of Explanation From Versa Networks SDWAN Topics:
The correct answers are B and D . In the exhibit, Enable Auto Switchover is not selected. However, the Failover Timeout value is configured as 300 seconds . Versa Director HA documentation states that the Failover Timeout is the timeout period before the standby Director node can promote itself to become the active Director node. Therefore, if the active or primary Director fails, the backup Director can automatically assume the active role after the failover condition and timeout are met.
The important distinction is that Auto Switchover controls revertive behavior after recovery, not the initial standby takeover during failure. Versa documentation explains that Director HA is non-revertive by default.
This means that when the designated master or primary Director comes back online after recovery, it is not automatically promoted back to active unless automatic switchover is enabled. To make the designated active Director automatically reclaim the active state after recovery, Enable Auto Switchover must be selected and the Auto Switchover Timeout must expire.
NEW QUESTION # 48
You are asked to ensure symmetric traffic flows between two SD-WAN branches. Which feature should be enabled to achieve this objective?
- A. Symmetric Routing
- B. Equal-Cost Multipath
- C. Packet Striping
- D. Symmetric Forwarding
Answer: D
Explanation:
Symmetric Forwarding is the correct Versa SD-WAN feature for ensuring that return traffic between SD- WAN branches follows the same SD-WAN path on which the forward traffic was received. Versa documentation for SD-WAN traffic steering describes Symmetric forwarding as the option that specifies the path for reverse-direction traffic, meaning whether traffic returning from the destination branch to the originating branch should be sent on the same path on which it arrived. It further states that enabling symmetric traffic forwarding determines the reverse path for traffic returning from the destination branch to the originating branch.
This is different from Symmetric Routing, which is a routing design goal or behavior, not the Versa SD- WAN forwarding-profile feature named in the product documentation. Equal-Cost Multipath can distribute flows across equal-cost routes, but it does not specifically guarantee that both directions of the same SD-WAN session use the same path. Packet Striping is used to split or distribute packets across multiple links for performance, not to enforce bidirectional path symmetry. Therefore, the verified Versa feature to enable is Symmetric Forwarding.
NEW QUESTION # 49
You have deployed a group of devices in Versa Director, and the field technicians have performed the onboarding tasks onsite. One of the devices has not finished the onboarding process and does not appear in the Appliances list in Versa Director. The onboarding VPN tunnel from the device to the Controller is up.
Which two actions would help you solve this problem? (Choose two.)
- A. Verify that the device is listed in the Connectors > Local > Resource Pool dashboard.
- B. Review the Unknown Devices dashboard in the Administration > Inventory menu.
- C. Use the Monitor dashboard in Versa Director to view the status of the missing device.
- D. View the Tasks list in Versa Director to see whether an error was encountered during the onboarding process.
Answer: B,D
Explanation:
The correct answers are A and C . If the onboarding VPN tunnel from the branch device to the Controller is up, the branch has reached at least the initial staging/control connectivity stage. Versa troubleshooting documentation explains that after a branch establishes IPsec connectivity to the Controller, the Controller sends a branch-connect notification to Versa Director. In response, Director pushes staging configuration and continues the onboarding lifecycle. If the expected later notification is not seen, the branch has not completed staging and further onboarding/debug steps are required.
The Tasks list in Versa Director is useful because device deployment and onboarding actions are executed as Director tasks. If template commit, workflow deployment, device claiming, or configuration push fails, the task output can show the error. The Unknown Devices dashboard is also relevant because a device that reaches the Controller but cannot be matched or fully associated with an expected workflow/appliance record may appear as an unknown device awaiting administrative review. The Monitor dashboard is not the best choice because the device is missing from the Appliances list and has not completed onboarding. Resource Pool is related to connector resources, not branch onboarding completion.
NEW QUESTION # 50
You need to quickly check interface administrative status, operational status, tenant ID, VRF, MAC address, and IP address on a VOS device. Which command should you use?
- A. show coredumps
- B. show interfaces brief
- C. show system storage
- D. show system package-info
Answer: B
Explanation:
The correct answer is A . Versa's handy CLI command reference lists show interfaces brief as the command used to view a list of interfaces along with their MAC addresses, operational and administrative status, tenant ID, VRF, and IP addresses. This is one of the first commands administrators run when validating device bring- up, staging interface assignment, WAN/LAN mapping, or whether a template applied interface addressing as expected.
For deeper interface troubleshooting, show interfaces detail provides additional information such as interface index, host interface, MTU, speed and duplex settings, RX/TX errors, and bridge information. However, for a quick overview of state and addressing across interfaces, show interfaces brief is the correct choice.
show system package-info identifies the running VOS software package. show system storage reports system storage resources. show coredumps shows generated core files. These are valuable operational commands, but they do not provide the requested interface status and addressing summary.
NEW QUESTION # 51
An SD-WAN branch is deployed behind a NAT device. In the VSM local-tunnel-site output, which field or flag indicates that a WAN link is behind NAT?
- A. Tenant ID only
- B. WAN lcl vrf-id only
- C. WAN lcl link behind NAT or BN flag
- D. Neighbour site type only
Answer: C
Explanation:
The correct answer is A . Versa SD-WAN data-path troubleshooting documentation shows the VSM local- tunnel-site output and includes a legend in which BN means Behind NAT . In the WAN local link details, the output also displays a field named WAN lcl link behind NAT , with values such as 1 or 0, and link flags including [ BN CT PT SLA-P ] when the WAN link is behind NAT.
This information is important because NAT status affects how SD-WAN tunnel endpoints are discovered and how public and private transport addresses are represented. The same output includes both public and private WAN link addresses, making it useful for troubleshooting sites behind NAT, stale tunnel endpoints, or incorrect public-address learning.
WAN lcl vrf-id identifies the local transport routing instance ID, not NAT status. Tenant ID identifies the tenant context. Neighbour site type identifies whether the remote endpoint is a Controller, hub, or SD-WAN site. None of those fields specifically confirms whether the local WAN transport is behind NAT.
NEW QUESTION # 52
During onboarding, Versa Director shows the first branch-connect notification for a new CPE, but no later staged branch-connect notification appears. Which troubleshooting area should be investigated first?
- A. URL filtering database download status
- B. Versa Analytics log collector disk usage
- C. Data path or IPsec connectivity from the branch to the Controller
- D. LDAP authentication configuration on the tenant
Answer: C
Explanation:
The correct answer is B . Versa branch lifecycle notifications are generated at different stages of onboarding.
The first notification indicates that the branch connected using factory-default configuration. After that notification, Versa Director pushes the staging configuration to the branch and requests a reboot. After rebooting with staging configuration, the branch should connect again to the Controller, and a later branch- connect notification should appear.
If this later staged connection notification does not appear, Versa's troubleshooting guidance says to debug either the data path or IPsec connectivity from the branch to the Controller. This makes sense because the branch must have working transport reachability and IKE/IPsec establishment toward the Controller before it can continue the SD-WAN lifecycle.
Analytics disk usage, LDAP authentication, and URL filtering are not part of the branch staging control path. They may affect monitoring, user identity, or security inspection after the site is operational, but they do not explain why the branch stops after the initial factory-default onboarding notification.
NEW QUESTION # 53
Which two methods would be used to upgrade deployed VOS branch devices? (Choose two.)
- A. Upload the new software package to Versa Director, then use the Appliances dashboard to upgrade the devices.
- B. Upload the new software package to Versa Director, then use the System > Director Upgrade dashboard to upgrade the devices.
- C. Copy the .bin file to the VOS device to the appropriate path and upgrade the device using the CLI.
- D. Update the template workflow and select the new software package in the Preferred Software Version field, redeploy the workflow, and commit the template.
Answer: A,C
Explanation:
The correct answers are A and C . Versa supports upgrading deployed VOS branch devices either directly on the VOS appliance or centrally through Versa Director. The Director-based method is performed from the Administration > Appliances area: Versa documentation says to select one or more Controller nodes or VOS devices, click the Upgrade Selected Appliances icon, choose the software image package, and proceed with the appliance upgrade. The same upgrade procedure is referenced for remaining VOS branch devices, including the option to upgrade branches individually or all at once.
A CLI-based upgrade using a software .bin package is also a valid operational method when the image is copied to the device and installed locally, particularly for controlled or recovery-style maintenance.
Option B is not the best answer for already deployed branch upgrades because the Preferred Software Version field applies to zero-touch provisioning; Versa states that during ZTP, Director upgrades a branch to the preferred version if applicable. That setting influences onboarding behavior, not the normal upgrade workflow for already deployed branches. Option D is incorrect because System > Director Upgrade is used to upgrade the Versa Director node itself, not VOS branch appliances.
NEW QUESTION # 54
......
VNX301 Actual Questions Answers PDF 100% Cover Real Exam Questions: https://www.testinsides.top/VNX301-dumps-review.html